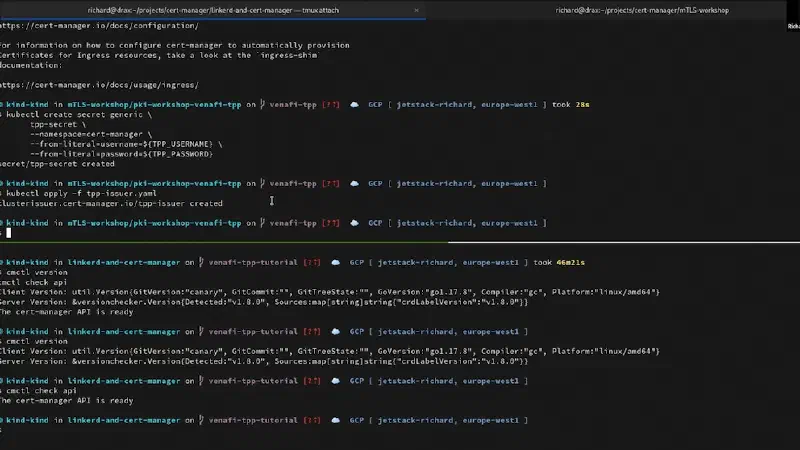
Enterprise PKI in the cloud-native world with Linkerd and cert-manager
Migrating an existing enterprise PKI to Kubernetes can be daunting — there are so many moving parts to achieving trust across boundaries!
Monthly live workshops providing hands-on training on Linkerd and related CNCF projects.
Migrating an existing enterprise PKI to Kubernetes can be daunting — there are so many moving parts to achieving trust across boundaries!
Whether for disaster recovery, multi-tenancy, or user-facing latency, deploying applications across multiple clusters is an increasingly common approach to Kubernetes. Unfortunately, while Kubernetes gives you many reasons to run multiple clusters, it provides you with very little help in doing so.
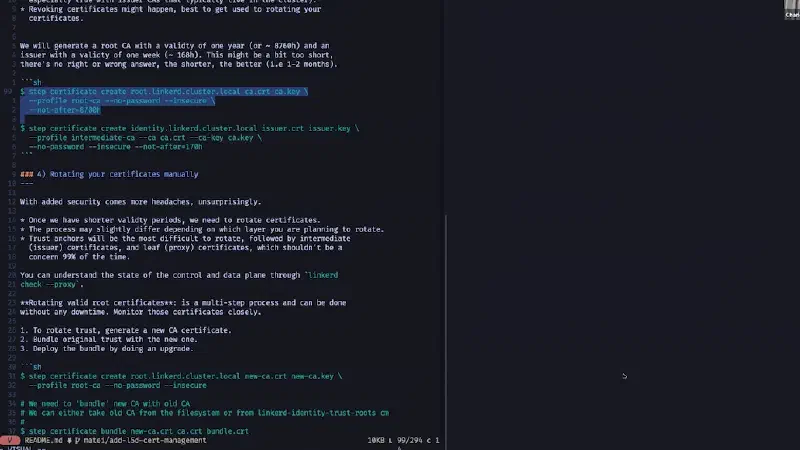
In this workshop, we'll cover the basics of TLS certificate management in Linkerd. While Linkerd issues, rotates, and validates per-pod TLS certificates automatically, the treatment of per-cluster issuer credentials and global trust root credentials can differ based on security goals and organizational policies.
In this workshop, we encrypt app calls end-to-end with Emissary-ingress, Linkerd, Kubernetes, and Envoy — four CNCF projects. Emissary-ingress and Linkerd team members will share best practices to get ingress TLS, in-cluster mTLS, advanced L7 routing, rate limiting, embedded authentication, and more.
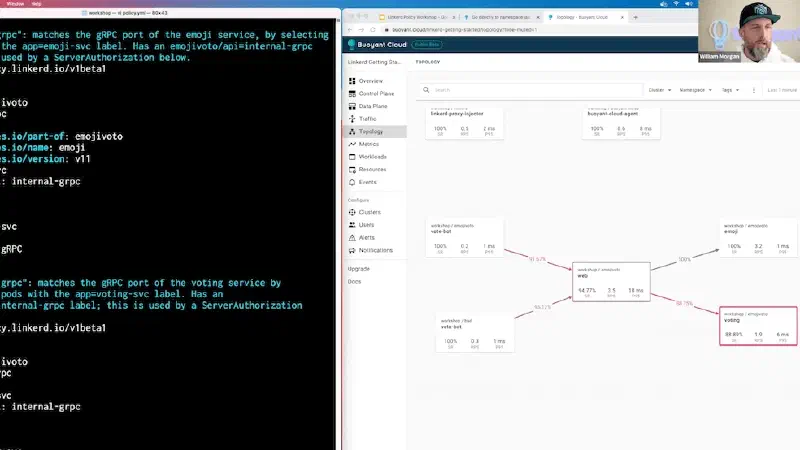
In this hands-on workshop, we cover the basics of locking down in-cluster network traffic using the new traffic policies introduced in Linkerd 2.11.
In this hands-on session, we’ll walk you through the basics of what you need to know to successfully deploy and operate Linkerd in production environments — from operational monitoring to setting up TLS certificates, per-route metrics, fine-grained traffic policy, & more.
Mutual TLS (mTLS) is a hot topic in the Kubernetes world, especially for anyone tasked with getting “encryption in transit” for their applications. In this workshop, we give you a solid understanding of what mTLS is, how it works, and how it compares to alternatives.