Federated Anchors: Simplifying Linkerd Multicluster Trust and Certificate Rotation
Rotating a shared trust anchor across Linkerd clusters is painful. Federated anchors add per-cluster anchors so you can rotate one cluster at a time.
developers about the Linkerd service mesh, Kubernetes, and cloud-native development in general. He has spent four decades in software engineering - from the kernel up through distributed applications, with a common thread of communications and security throughout - and is the original author and a maintainer of the Emissary-ingress API gateway. He is most easily found as @flynn on the CNCF or Linkerd Slacks.
Rotating a shared trust anchor across Linkerd clusters is painful. Federated anchors add per-cluster anchors so you can rotate one cluster at a time.
Linkerd ❤️ Gateway API, so it's important that we stay conformant. Learn more about gRPC, protocol declaration, detection, and how it all recently went awry.
One of the things that differentiates EKS, Amazon’s managed Kubernetes service, from its peers is its near insistence that clusters must always span multiple availability zones (AZs).
Welcome to EKS! If you’re familiar with Kubernetes but new to the world of AWS and specifically Amazon’s managed Kubernetes service, this is the guide for you.
Linkerd 2.14 reached its end of life on June 1, 2025, and we strongly recommend that you upgrade.
Over the last year or so, we’ve seen a lot of confusion about “sidecars or sidecarless” in the context of service meshes. This architectural choice turns out to be very important – not because of sidecars per se, but because it deeply affects how the mesh approaches sharing and multi-tenancy.
A great many Linkerd installations use cert-manager and trust-manager to excellent effect, and you can read all about how to set this up in the Linkerd documentation. Recently, though, cert-manager made a change that has the potential to disrupt Linkerd installations with a particularly subtle misconfiguration.
In this guide we'll walk you through a task that is increasingly common in the Kubernetes space: migrating an existing Istio deployment to Linkerd.
Any organization working in the cloud has to manage multiple, complex challenges to security and reliability, while keeping a tight rein on costs. Your brand’s reputation depends on managing these challenges with aplomb, ensuring that you handle threats and failures quickly, transparently, and efficiently.
Today, we are excited to announce the availability of Linkerd as a fully supported service mesh on Microsoft's newly-announced Azure Linux distribution. This collaboration between Buoyant and Microsoft means that Azure Linux customers can now take full advantage of Linkerd’s security, reliability, and observability features.
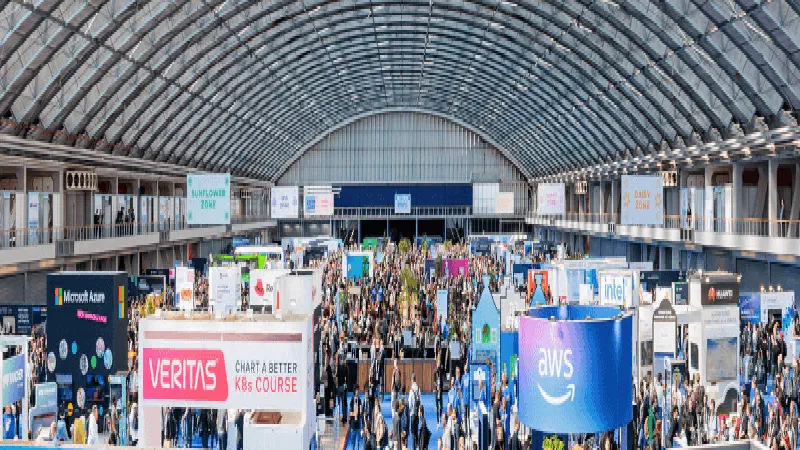
KubeCon and Linkerd Day Europe in Amsterdam wrapped a few weeks ago. This KubeCon was very special. We hosted the first-ever Linkerd Day, with 100% end user talks.
The cloud native ecosystem with Kubernetes at its core has transformed how organizations deploy and operate applications in the cloud. One part of the stack has been getting particular traction from security professionals lately: the service mesh—an infrastructure layer that manages and controls network communication between Kubernetes-based microservices.